Technology
MALICIOUS 'CLAUDE CODE' COPY SLIPPED INTO CURSOR'S MARKETPLACE FOR 11 HOURS
A malicious copy of extension versions 2.1.312 and 2.1.313 was available in Cursor's marketplace for about 11 hours on October 29, Cursor said — while Microsoft separately detailed intrusions posing as IT support.
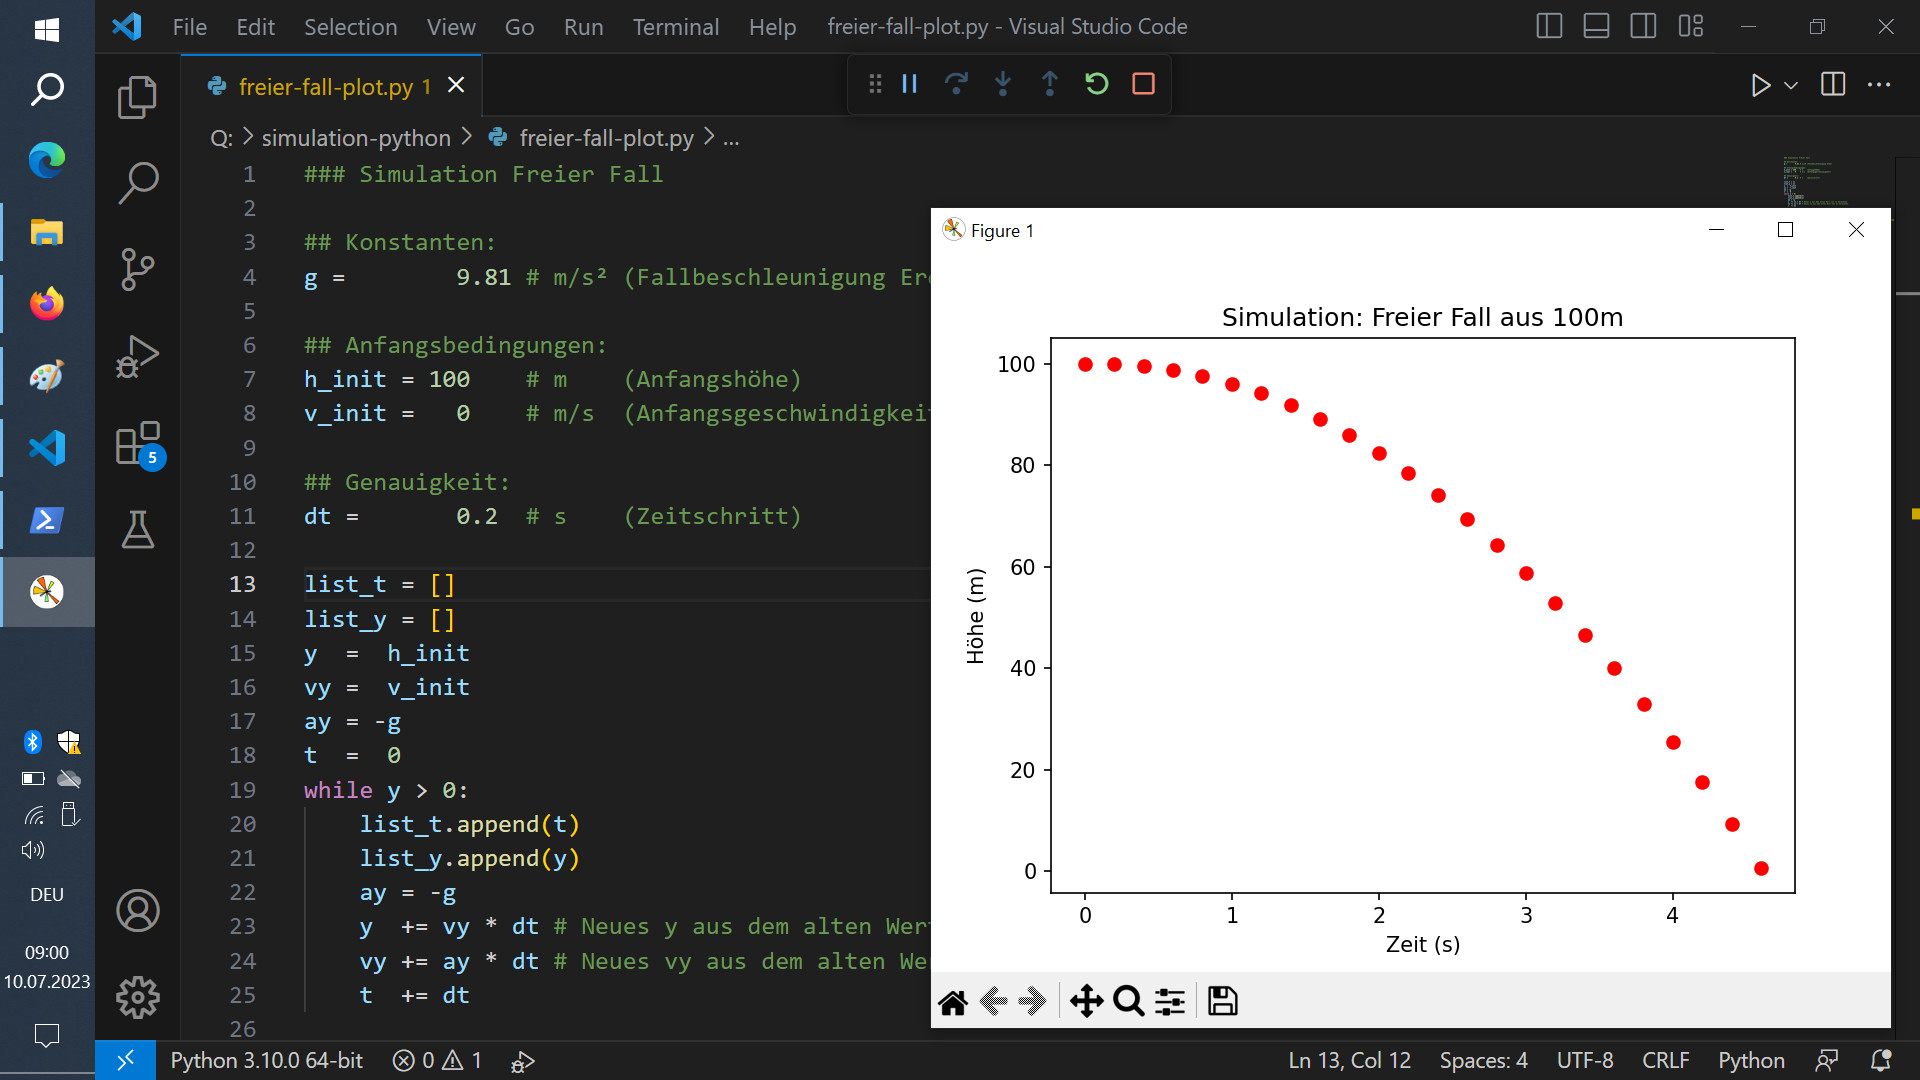
Cursor said a malicious copy of extension versions 2.1.312 and 2.1.313 was available in its marketplace from about 2:27 a.m. to 1:35 p.m. Pacific time on October 29, and Microsoft independently analyzed the package.
Microsoft's October 30 research also described two investigated intrusions in which attackers posed as IT support in Teams and persuaded users to grant remote access, primarily through Quick Assist.
Separately, Anthropic researchers demonstrated CVE-2026-98432, a Linux kernel flaw, enabling remote root access on a server running a Multipath TCP (MPTCP) listener.
BleepingComputer reported the flaw affects kernels back to version 4.4, with the kernel's CVE team rating it 9.8 out of 10, though Red Hat initially rated it lower as mainly a crash risk.
The disclosures cap a busy week for software supply-chain security, as developers were urged to verify extension publishers before installing updates.
Reporting: Your Cyber Brief
Spot an error? Orbit News corrects articles promptly and notes the correction in the article. See our Editorial Policy, or flag an error by messaging us on Facebook, X, or Instagram.
Related from Orbit News
APPLE CAVES AT LAST: FIRST TOUCHSCREEN MACBOOK PRO ARRIVES WITH PROLED DISPLAY
Technology · Oct 31, 2026
FCC CLEARS AMAZON'S $11.5 BILLION GLOBALSTAR DEAL IN SATELLITE RACE WITH STARLINK
Technology · Oct 31, 2026